Fraud at machine speed: how fleets and station operators are adapting to faster threats
Fuel price volatility, AI-assisted attacks and slow-moving rulebooks are reshaping fraud risk for fleet and mobility payment providers. We spoke with Deon Louw, Senior Fraud and Risk Manager at The ai Corporation, about where the real exposure sits and what a modern defense looks like.
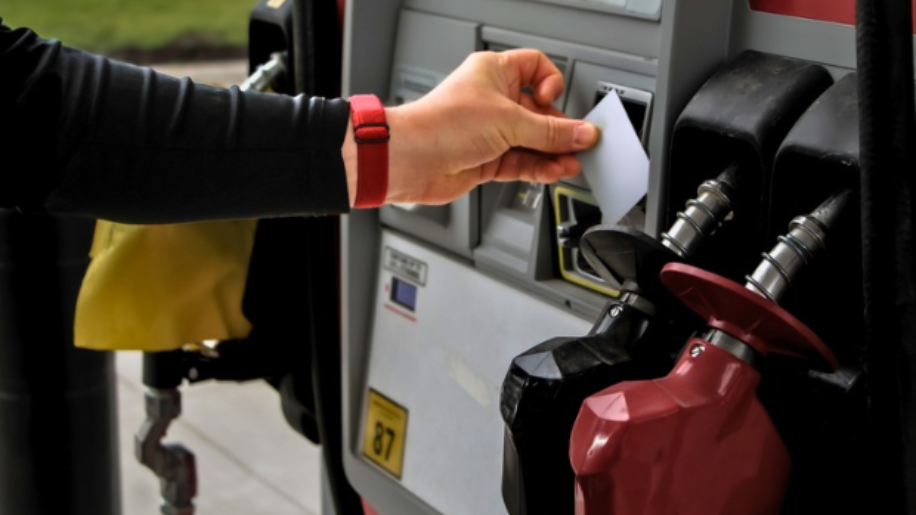
In fleets and mobility, fraud often hides inside transactions that look perfectly routine, rarely looking like fraud at first glance. A fuel card is a payment instrument handed to hundreds or thousands of drivers, used at unattended pumps across wide networks, often outside office hours, with spend spread across many small, routine transactions. That leaves the sector exposed on several fronts at once: internal misuse such as personal refuels or shared cards and PINs, external attacks such as skimming and card cloning, and authorization decisions that issuers must take in milliseconds without stranding a legitimate driver at the pump. Effective fraud management here depends on keeping three forces in balance: acceptable losses, the impact on customers, and the capacity to investigate what gets flagged.
2026 has made that balance harder to hold. Fuel prices surged after the outbreak of the Iran war and costs now top the American Transportation Research Institute's ranking of trucking industry concerns. At the same time, AI is reshaping fraud on both sides of the transaction, a trend Visa flagged in its spring threats report and one that October's PHP2Shell vulnerabilities made tangible. In this Q&A, Deon Louw, Senior Fraud and Risk Manager at The ai Corporation, draws on more than 20 years in card, payments and transactional fraud to explain where fleet operators are most exposed, how detection has evolved, and why speed now matters as much as accuracy.
MobilityPlaza. Higher fuel prices make every misused litre more expensive, with risks of fuel-related theft and fraud rising alongside them. From your experience, which fraud challenges cost fleet managers the most today, and which do they tend to underestimate?
Deon Louw. Traditional fraud remains the immediate concern in internal combustion engine (ICE) fleets, even as EV charging expands and brings a growing fraud challenge. Swapped, lost, or stolen cases account for 70% of cases, making them the largest category by volume; however, that alone does not establish their share of financial losses. Abuse involving genuine payment credentials is the second-largest category, at 17% of cases. This is particularly concerning because it uses the original transaction mechanism, and management controls may be known and therefore circumvented. Research published by Cubic 3 in April 2026, based on a survey of 2,000 UK drivers, found that one in ten respondents admitted falsifying fuel expenses at least once. This is a self-reported survey finding about fuel expenses, not a measured fleet-card fraud-loss rate.
For fleet managers, the priority remains tackling fuel fraud today while preparing for the additional risks of electrification. The transition does not replace the existing fraud challenge: as EVs become more prevalent, fleets need to maintain their fuel-card controls while extending fraud management to charging. The aim is to protect both sides of that transition, rather than shift attention away from the fuel losses they already face.
For fuel fraud, the immediate challenge is to strengthen real-time monitoring by bringing the right information into each decision. That means combining transaction data with information from mobile applications, other relevant inputs and available level 3 purchase data within a real-time fraud monitoring system. Traditional systems often rely on rigid data-field structures, which can limit effective monitoring and fraud management. As fleets transition and EV charging becomes more prevalent, those systems also need to accommodate different transaction journeys. The traditional pattern of a single product used by a single vehicle may no longer apply: a vehicle may use both conventional fuel and EV charging. The requirement is to extend fraud controls to these additional journeys without weakening protection against established fuel fraud.
MP. Lost or stolen cards are more likely to trigger an alert, but abuse of genuine can look like normal spending. How do you spot it, and what can fleet managers do about it?
DL. Abuse of genuine fraud includes cases like people fuelling other vehicles on fleet cards or drivers sharing cards and PINs to illegally extract value from the ecosystem. The only way to tackle it is to monitor litres used and look for any change in product or site. It is especially hard to spot because offenders usually keep to the same sites and buy the same product as the original vehicle; anything different would be too obvious. We do see a slight rise in usage. Some people conceal it well, but external factors can expose them: they may lose count of how often they have filled the business vehicle and their own, or a site may report that the registration number did not match the card. Overall, abuse of genuine is one of the hardest types of fraud to identify and match.
One avenue we encourage fleet managers to pursue is activating and deactivating cards for each use, where possible. It adds an administrative burden, but we’re working on automation to make it easier and faster in the future. You activate the card much like a single-use virtual card from a bank: it can be used, then locked again afterwards. It has its pros and cons. Connectivity may not always be available, and a driver with an emergency at two o’clock in the morning may not be able to reach their fleet manager. But within those limits, it’s an effective way to manage the risk.
MP. Fraud has always been a moving target. How have fuel card issuers and fleet operators traditionally kept up? How much of that playbook still holds now with AI on both sides?
DL. The traditional fuel-card fraud playbook has not become obsolete: roughly 70–80% of the historical controls remain essential and form the foundation of prevention. What AI changes is how quickly and at what scale those controls can be supported by more sophisticated risk detection. For issuers and fleet operators, that means helping alert-management teams reduce noise and concentrate on critical cases. But the same technology also enables fraudsters to adapt and make their attacks more convincing. The task is to strengthen the existing playbook, not assume that adding AI replaces it.
For fleet and fuel cards, the priority is to make existing controls more intelligent across prevention, detection and response - not simply to replace them. That requires strong governance, quality data, human expertise and AI-driven analytics working within a single fraud management strategy. The organisations that succeed will be those that combine these elements effectively, rather than those that deploy the most AI. Rely on the machine alone at your peril!
MP. Speed works both ways. In October, two critical PHP flaws found with AI tools leaked before patches were out, and attackers moved within hours. What does that tell the sector about how fast threats now move?
DL. The lesson extends beyond fleet and mobility payments to any organisation using PHP: overlooked infrastructure can create serious exposure, even where the wider environment is considered secure. It also shows how quickly threats can move beyond traditional governance cycles, leaving organisations struggling to patch or mitigate them in time. The response needs two time horizons. First, move from periodic security reviews and reactive fraud monitoring towards continuous, AI-assisted risk management, with the ability to identify, assess and respond quickly when a vulnerability becomes known. Second, consider future threats when designing application features and deploying technology today, including how those systems will be managed as AI capabilities advance.
MP. Does an episode like that bring fraud and cybersecurity teams closer together?
DL. Traditionally, you’ll still find the two teams separated. Cybersecurity looks at the system and system-related risks, with both an internal and external focus, whereas fraud teams generally focus externally. But the two are increasingly aligned, especially when incidents such as internal fraud occur. For example, if someone within the organisation manipulates the system to commit fraud against customer accounts, IT teams may not have expertise in the mechanisms or channels used. They rely on the fraud and investigation teams to support them and provide evidence, so they can follow the trail and identify where the weaknesses were. In short, it reinforces the need for a collaborative team approach.
The cyber teams monitor the landscape and run environmental scans to highlight anomalies and/or suspicious behaviour. If they see anything concerning, they come and tell us. Take PHP2Shell, which affected websites and services across many companies. When our security team told us there may or may not be an impact down the line, we discussed how we could support the business, keeping disruptions to a minimum while still preventing fraud. While they fixed and patched third-party or other affected systems, we made sure we could still mitigate and manage risk for our customers. We reverted to some manual systems, but that is exactly why we have playbooks and keep them relevant for situations like this. I’m now seeing much more collaboration between IT security and fraud teams, with a clear understanding of how each team’s work affects the other.
MP. PHP2Shell wasn't the only recent warning. In the last few weeks, attackers took control of refrigeration systems in hundreds of French supermarkets, and stores in other European countries have since reported similar incidents. What do attacks like these say about the risks hiding in older systems?
DL. The concern is that older systems can contain vulnerabilities buried beneath years of code, while the people who understood that code have moved on. Those risks may not be visible in day-to-day operations, but they still need attention. The response cannot simply be to wait for the next major system upgrade.
At The ai Corporation, our approach centres on continual improvement, supported by continuous integration and continuous delivery (CI/CD). The aim is to shorten release cycles so changes can be built, tested, and made ready for deployment more quickly, especially when security concerns emerge. Automated builds and testing support that approach, alongside security checks and human review.
That does not mean deploying every change automatically into a customer’s live environment. Production releases still need the appropriate approvals, validation and recovery plans. When a security issue arises, the priority should be to assess the risk and move the necessary fix through those controls promptly. It is about making change faster and more responsive without sacrificing the safeguards that payment systems require.
MP. Several of the risks we’ve discussed start with weaknesses in the technology itself. How does The ai Corporation approach security in its own products?
DL. Our approach starts with defence in depth, building security into our products and processes from design through to deployment. That combines new agentic capabilities with SAST (Static Application Security Testing) and DAST (Dynamic Application Security Testing). Syndicates are exploiting vulnerabilities faster than governance and regulation can respond, so security must remain central to how we develop and operate our solutions. The ai Corporation has recently obtained ISO 27001 certification alongside SOC 1 and SOC 2 certifications. We regard those credentials as a starting point for ongoing security work, not the endpoint.
Our in-house ai Fraud Managed Service (aiFMS) brings together alert-management specialists, fraud analysts and data scientists to develop a tailored fraud strategy aligned with each customer's business objectives. The team manages the deployment of approved rules within aiRiskNet®, combining human expertise with the speed and scale of AI-driven automation. The aim is to help customers detect more fraud, respond faster as threats change and continuously strengthen their strategy without increasing their operational workload.
MP. And on the fraud side, how do you help fleet and mobility payment providers keep pace with the threats we’ve been discussing?
DL. aiRiskNet® can operate independently or integrate with the aiEazyFuel® mobility payments platform to protect mobility payments from fraud. It brings transaction monitoring, rules-based decisioning, machine-learning scoring and automated fraud strategy optimisation together in a single solution. The ai Corporation's intelligent fraud management platform has protected global banking and other institutions for almost 30 years, processing billions of transactions annually.
There are two complementary processes. The aiFMS team uses machine-learning models to identify complex patterns and emerging risks and provide a risk score for each transaction. Separately, continuous analysis of transaction behaviour generates, tests and recommends optimised rules and model strategies as trends evolve. Transaction scoring supports individual risk decisions; strategy recommendations support the ongoing improvement of fraud controls.
The aim is to help organisations protect fuel payments today and operate confidently as fleet payments expand into open-loop payments, digital wallets, EV charging and broader mobility services. We continuously modernise our technology stack and accommodate new data streams for fraud monitoring, supporting real-time response through AI-driven fraud detection, adaptive controls and integrated fleet payment processing. It is not simply about detecting fraud faster: it is about extending protection as payment journeys change, without losing focus on established fuel-fraud risks.
MP. Europe’s new payments rules (PSD3 and the PSR) won’t apply until around 2028, and the AI Act’s high-risk obligations have moved to late 2027. With attackers working in hours and rulebooks in years, how is the industry able to fill this gap on its own?
DL. Yes, there is a gap, and it is widening. The fleet and mobility payments sector cannot wait for future rulebooks to manage present risks. Attackers operate in hours, technology evolves in months, and regulation typically moves in years. Resilient organisations treat compliance as the minimum baseline and build adaptive, intelligence-led controls around it. Cost remains a real constraint and may be prohibitive, making agility essential: organisations need to prioritise their efforts and redirect them as threats change, rather than assume they can address every risk at once.
The opportunity is to innovate responsibly ahead of compliance, rather than treat compliance alone as a competitive advantage in fraud prevention. One way to strengthen resilience is through authorised internal security testing that identifies vulnerabilities so teams can address them. As AI capabilities advance, this kind of proactive work may become increasingly important in helping organisations stay ahead of threats.
MP. If that gap is filled with more automation, where should the human stay in the loop?
DL. People need to remain responsible for rare, ambiguous, high-impact decisions that require judgement, context, and accountability. AI can handle routine decisions at scale and help teams focus their attention where human expertise adds the most value. For fleet and mobility payments organisations, the aim is not to remove people from fraud management, but to deploy them more effectively. Human intervention may become less frequent as automation develops, but the importance and impact of that oversight will increase.
Automation needs clear guardrails defining what AI can decide and where its authority ends. Anything outside those limits needs to be treated as an exception, with a person responsible for reviewing the case and making the final decision. That keeps human accountability explicit as more of the fraud-management process becomes automated.